Bubbles — signal by topic
size = articles (7d) · editorials by Cayce127 articles in security — bigger & brighter = stronger signal
Resurrected PHP binding for secp256k1
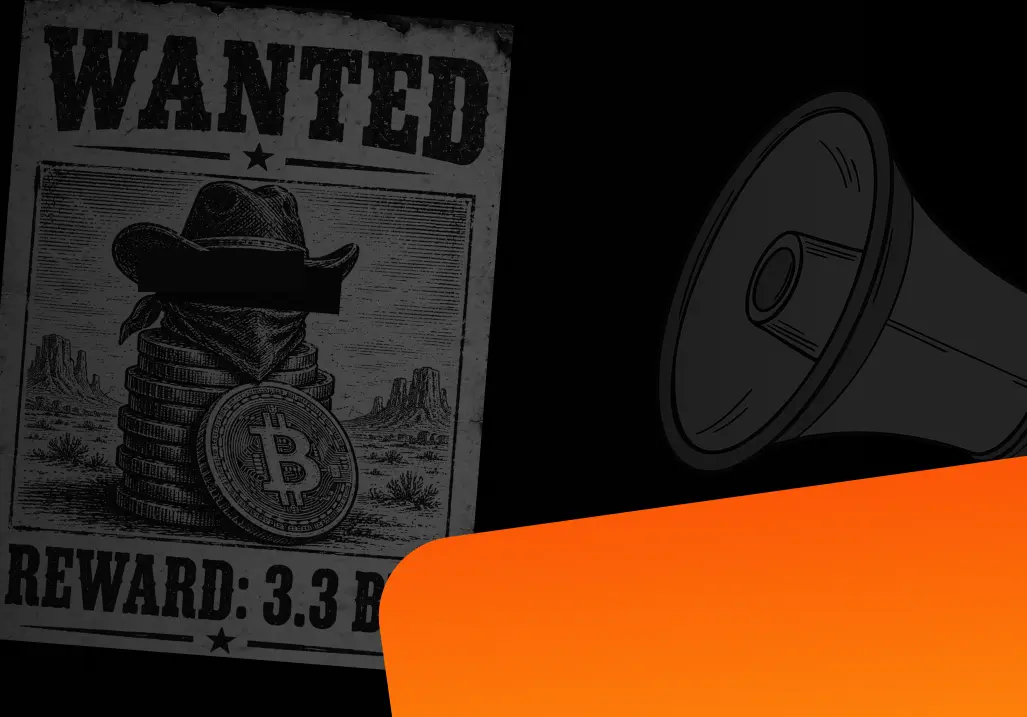
The September 19 Attack — facts, full story, and a bounty (up to 3.3BTC)
Blink post-mortem: on 19 September 2026 an attacker used a flaw in how its admin tools checked permissions to grant admin powers to a free account. 6.61 BTC taken from 24 accounts (22 customers). The nine accounts with 2FA lost nothing — all 18 attempts refused. Cold storage and non-custodial accounts untouched. Every balance restored on 24 September, paid by shareholders. The flaw had been open since October 2023. 50% bounty announced (up to 3.3 BTC).
A wrench attack, second by second
Bitbox 02 Nova: Hardware wallet with lightning? New tutorial and breakdown.
The article offers a comprehensive tutorial and breakdown of the BitBox02 Nova hardware wallet, focusing intently on its capabilities and integration with the Bitcoin Lightning Network. It likely delves into the practical aspects of setting up and using the BitBox02 Nova for secure self-custody of Bitcoin, highlighting how its Lightning features enable faster, more efficient, and cost-effective transactions. The content probably guides users through specific steps to configure Lightning functionality, manage their Bitcoin funds directly from the hardware wallet, and strengthen their operational security and privacy practices. This resource would be valuable for Bitcoiners seeking to enhance their self-sovereignty through robust hardware wallet solutions and leverage the advanced payment capabilities of the Lightning Network.
BISQ Release v1.10.9 w/ important security update fixed vulnerabilities
32d
Bitcoin Optech Newsletter #425
This week's Bitcoin Optech Newsletter #425 highlights two critical denial-of-service (DoS) vulnerabilities affecting older versions of Eclair (v0.13.1 and earlier), which have since been fixed in v0.14.0. The first vulnerability stemmed from inefficient feature bit parsing, where a single maximum-length init message could allocate 300 MB of memory and occupy a parsing thread for 300 ms, enabling attackers to quickly disconnect peers and exhaust memory. This was discovered using the `smite` LN fuzzer. The second DoS flaw was in gossip queries, where zlib decompression of legacy `query_short_channel_ids` messages lacked an output limit, allowing a 64 KB message to expand to 64 MB, potentially taking nodes offline. Both attacks required only a BOLT8 handshake. The newsletter also outlines a proposal for secure wallet label synchronization across devices and regular updates on Bitcoin consensus rule discussions and infrastructure software changes.
"Don't collect what you can't protect" - Tabconf T shirt giveaway design #4
The article title, "Don't collect what you can't protect" - Tabconf T shirt giveaway design #4, succinctly captures a fundamental principle within the Bitcoin community: the absolute necessity of self-custody and robust personal security. Originating from Tabconf, a renowned Bitcoin-only conference, this slogan functions as a vital admonition for Bitcoin holders to assume full responsibility for the protection of their digital assets. It implicitly warns against the inherent risks associated with entrusting one's Bitcoin to third-party custodians, where the user relinquishes control over their private keys, thereby reinforcing the well-known Bitcoin maxim, "not your keys, not your coins." The context of this being a design for a T-shirt giveaway at the conference suggests a deliberate effort to propagate this foundational security principle widely amongst participants and the broader Bitcoin ecosystem. This reinforces best practices for asset protection against potential threats such as theft, loss, or seizure. Although the article content is merely listed as "Comments," the impactful title alone communicates a potent message concerning operational security and the sovereign right and responsibility to protect one's own wealth in the decentralized Bitcoin network.
loading payment rails…